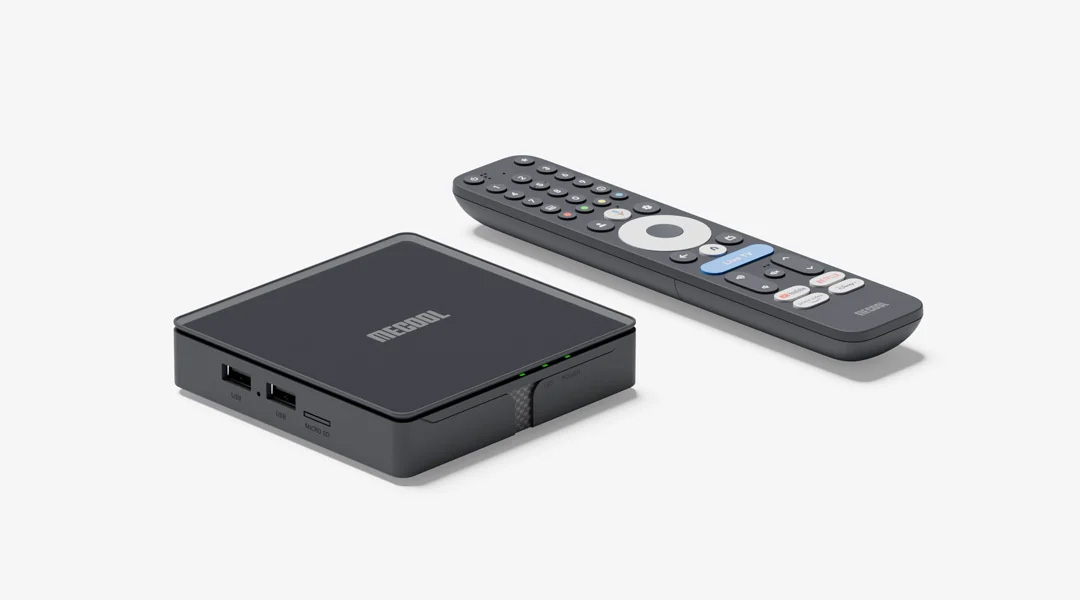
Google says it dismantled x.cpe, a botnet that ran on more than 1.3 million Android TV devices, according to its Threat Intelligence Group. The devices were Google-certified boxes, and Google says its screening process missed the malware because of "obfuscation techniques" used by Shenzhen-based Videostrong Technology.
Google's blog post describes x.cpe as a malware platform that grew from a single-stage dropper into a modular three-stage system. Operators sold access to third parties. Most of the compromised boxes were sold under the MECOOL brand.
According to Google, a stub application named x.cpe or com.oemservice contacted operators after devices came online. The stub had no malicious code of its own, but it held system-level permissions that let operators install malware modules. It also disabled Play Protect, Google's malware scanner, so the installed packages were not flagged.
Google found that most infected boxes ran residential proxies that routed large volumes of traffic, or modules that committed ad fraud. Google also reported that Videostrong had full access to the devices, allowing it to run terminal commands, capture screens, and probe other devices on local networks. Google says it observed this activity in real time.
Google worked with Japan's National Police Agency, Synthient, and Trend Micro. It took legal action to shut down domains and servers Videostrong used, including command-and-control servers tied to other malware campaigns. Google estimates Videostrong has been cut off from about 10 million compromised devices.
Play Protect remains disabled on affected devices, and the inert malware modules remain installed as system apps. Users cannot easily remove them. Synthient published a list of 182 device model names linked to the botnet. Trend Micro counted 1,472,554 infected devices, higher than Google's estimate. Most were in Brazil, Malaysia, Iraq, Mexico, and Taiwan, with tens of thousands in the US, Germany, the UK, Australia, and Canada.
Google ended its relationship with Videostrong and any subsidiaries, barring them from Android apps and services. Google says it is updating its certification process to close the loophole. According to the report, Videostrong could still sell malicious uncertified boxes under other brands.